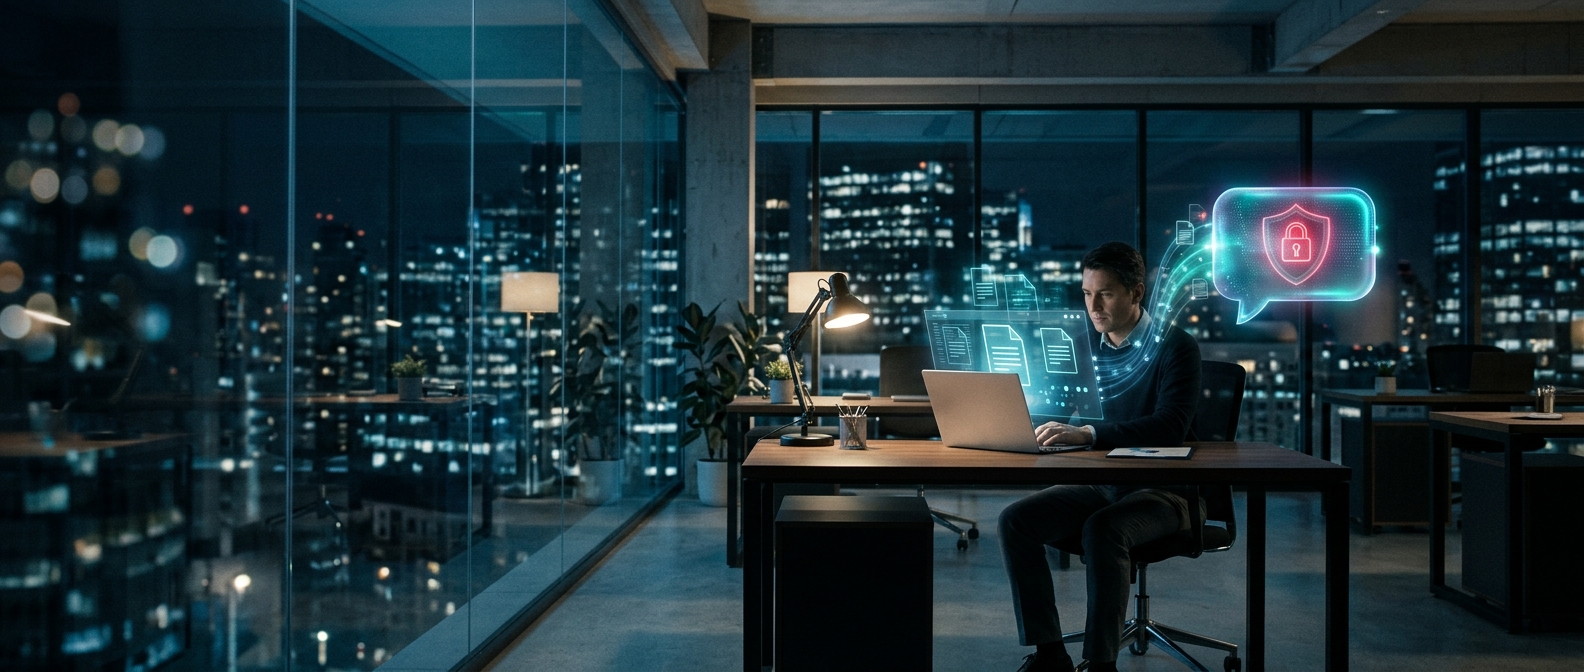
It is 11 pm, two hours before a client deadline. A junior analyst copies a client’s payroll extract into a public chatbot and asks it to “summarise the variances”. The summary looks great. However, the client’s salary data now sits on a third-party server, outside every contract the firm signed. This is how shadow AI data leaks happen, and in large audit, tax and consulting firms they are quietly becoming one of the biggest risks of the GenAI era.
Big Four-style firms hold some of the most sensitive data in the world: financial statements before they are published, M&A plans, payroll files and tax positions. As a result, one careless prompt can break client confidentiality, data protection law and professional ethics at the same time. In this guide, we explain why shadow AI is exploding, what the evidence says, and a practical seven-step playbook to adopt GenAI safely.
What Is Shadow AI, and Why Is It Exploding in Professional Services?
Shadow AI is the use of AI tools that the organisation has not approved, secured or monitored. It is the successor to “shadow IT”. Employees sign up with a personal email, paste in work content, and get an answer in seconds.
Professional services are especially exposed for three reasons:
- Deadline pressure. Billable-hour cultures reward speed, so people reach for whatever tool is fastest.
- Document-heavy work. Audits, due diligence and advisory reports involve huge volumes of text that GenAI summarises well.
- Uneven tooling. Approved enterprise AI tools often roll out slowly, team by team, while public tools are one click away.
The scale is significant. Reporting by CIO found that roughly half of employees are using unsanctioned AI tools, with enterprise leaders among the biggest culprits. Similarly, an Australian survey reported by IT Brief found that one in three workers upload sensitive data to AI tools.
The Real Risks of Shadow AI Data Leaks
Shadow AI data leaks are not just an IT problem. For an advisory firm, they create risk across five areas.
1. Client confidentiality and contract breach
Engagement letters usually restrict where client data can be processed. Pasting that data into a consumer chatbot may breach those terms, even if nothing is ever “hacked”.
2. Data protection and regulatory exposure
Personal data in HR, payroll or customer files falls under laws such as GDPR, Malaysia’s PDPA and similar regimes. Transferring it to an unvetted processor can trigger notification duties and fines.
3. Model training and retention
Some consumer AI services may keep prompts or use them to improve models, depending on settings and terms. Consequently, data can persist long after the employee closes the browser tab.
4. Higher breach costs
IBM’s 2025 Cost of a Data Breach research put shadow AI on the board agenda. As TechRepublic summarised, the report linked shadow AI and weak AI governance to costlier breaches. AI Business also highlighted that many organisations hit by AI-related incidents lacked proper AI access controls.
5. Hallucinated deliverables
The risk is not only data going out; it is also bad content coming in. Unchecked AI output can introduce invented facts, fake citations and wrong numbers into client reports.
Lessons from the Headlines
Two well-known cases show both sides of the risk.
Data going out. In 2023, Samsung restricted staff use of generative AI after engineers reportedly pasted sensitive source code into ChatGPT. Forbes covered the leak and the ban. The lesson: a ban came only after the damage was done.
Errors coming in. In 2025, a global professional services firm agreed to partially refund a government client after a commissioned report was found to contain AI-generated errors, including non-existent references. Fortune reported on the refund. The lesson: AI use must be disclosed, reviewed and owned by a human.
Together, these cases show that safe GenAI needs controls on both inputs and outputs.
The Regulatory Pressure: EU AI Act, NIST AI RMF and OWASP
Regulators and standards bodies are moving quickly. Firms should map their AI policy to three key references:
- The EU AI Act (Regulation (EU) 2024/1689) introduces risk-based obligations, AI literacy duties and transparency rules that apply in phases through 2026 and 2027.
- The NIST AI Risk Management Framework offers a practical structure to govern, map, measure and manage AI risk.
- The OWASP Top 10 for LLM Applications lists risks such as sensitive information disclosure and prompt injection.
For HR and people data specifically, our guide to AI in Human Resources: revolution or risk explores the ethical side in more depth.
A 7-Step Playbook to Prevent Shadow AI Data Leaks
Banning AI rarely works; people simply move to personal phones. Instead, the goal is to make the safe path the easy path.
Step 1: Provide an approved, enterprise-grade AI tool
Give every employee a licensed GenAI tool with contractual guarantees: no training on your data, defined retention, regional hosting and audit logs. If the approved tool is good, shadow use drops.
Step 2: Classify data and define “never paste” rules
Keep it simple: Public, Internal, Confidential and Restricted. State clearly that client-identifiable, personal and unpublished financial data must never go into unapproved tools.
Step 3: Deploy DLP and CASB controls on AI domains
Data loss prevention and cloud access security tools can detect, warn on or block sensitive uploads to known AI sites. In addition, a just-in-time warning teaches people at the exact moment of risk.
Step 4: Publish an approved AI tools catalogue
List which tools are approved, for which data classes, and how to request new ones. A fast approval path removes the main excuse for shadow AI.
Step 5: Teach prompt hygiene and redaction
Train staff to anonymise names, replace client identifiers and use synthetic samples. For example, “Company A” and rounded figures are usually enough for the AI to help.
Step 6: Keep a human in the loop for every deliverable
Require reviewers to verify facts, figures and citations in AI-assisted work. Also, disclose AI use to clients where contracts or professional standards require it.
Step 7: Build AI literacy, not just policy
A policy nobody reads changes nothing. Short, role-based training, real examples and leaders who model good behaviour make the difference.
The HR and People Angle: Building a Culture of Responsible AI
Shadow AI is ultimately a human behaviour problem. People cut corners when they are overloaded, which is why it links directly to the global toll of deadline-driven, burnout cultures. Therefore, HR, risk and IT must design AI governance together.
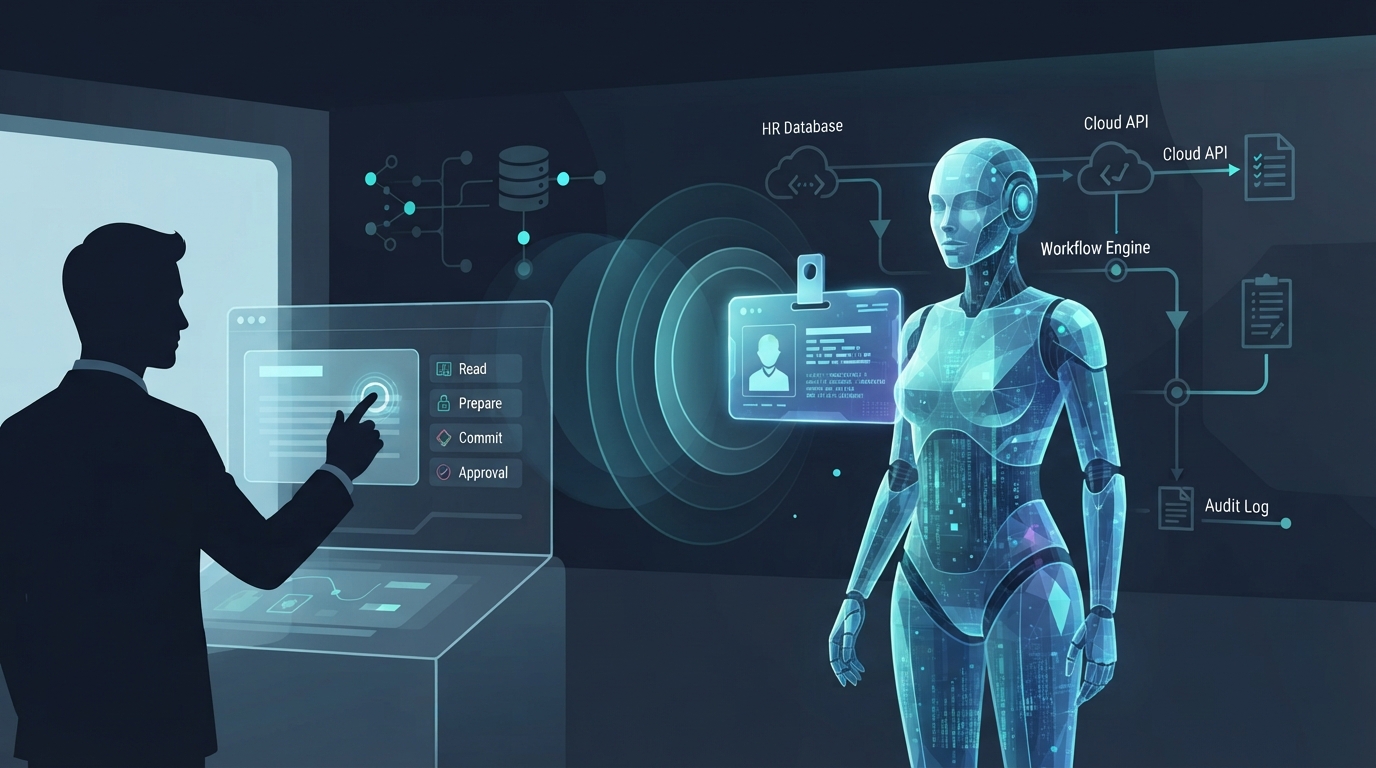
As AI agents start to act inside systems, the stakes rise further. Our articles on who owns the action when an AI agent changes HR data and how to control an AI coworker’s identity and access show why permissions and audit trails matter. Likewise, securing how AI agents connect to enterprise systems through MCP is quickly becoming part of the same conversation.
Quick Checklist for Safe GenAI Use
| Control | Owner | Status |
|---|---|---|
| Enterprise AI tool with no-training clause | IT / Procurement | ☐ |
| Data classification and “never paste” rules | Risk / Legal | ☐ |
| DLP and CASB rules on AI domains | Security | ☐ |
| Approved AI tools catalogue | IT | ☐ |
| Human review of AI-assisted deliverables | Engagement leaders | ☐ |
| Role-based AI literacy training | HR / L&D | ☐ |
Frequently Asked Questions
What are shadow AI data leaks?
They happen when employees put company or client data into AI tools that the organisation has not approved or secured, so the data leaves its control.
Should firms ban public AI tools?
Blanket bans tend to push usage underground. A better approach is to offer an approved tool, set clear data rules and monitor high-risk uploads.
Is enterprise AI automatically safe?
No. It reduces risk, but firms still need access controls, logging, data rules and human review of outputs.
Who should own AI governance?
It works best as a shared model across risk, IT, legal and HR, with clear accountability at leadership level.
Is Your Firm Ready for Safe GenAI?
💬 Comment: Does your organisation have an approved AI tools policy yet? Tell us below.
🔁 Share: Send this playbook to your risk, IT and HR leaders.
📩 Subscribe: Get weekly insights on AI, HR tech and integrations from ITPro.Works.
🤝 Talk to us: Need help designing AI-safe HR data integrations? Get in touch.
Conclusion
GenAI can make professional services faster and sharper, but only if firms control what goes in and what comes out. Shadow AI data leaks are preventable. With an approved tool, clear data rules, smart technical controls and a culture of responsible use, firms can protect client trust while still capturing the value of AI. The firms that act now will set the standard; the rest will learn from the headlines.